Google has confirmed that one of its Android manufacturing partners deliberately built a backdoor into 1.3 million devices and used them as a botnet. The company named Videostrong Technology Co., a Shenzhen-based manufacturer, and said it has now dismantled the malware and cut ties with the company.
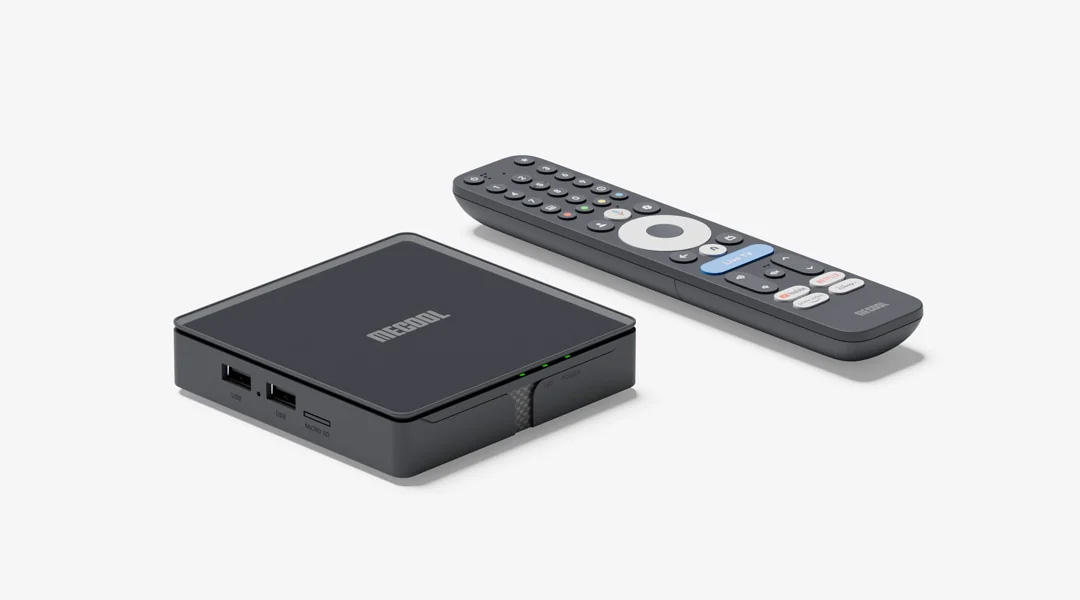
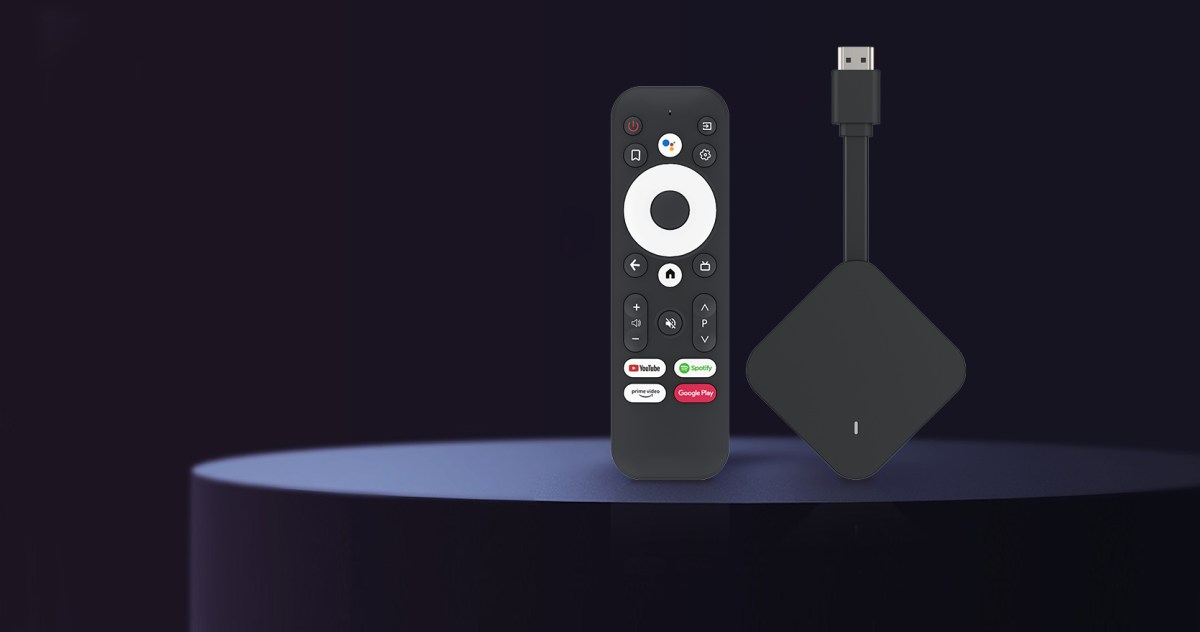
The affected machines were mainly Android TV set-top boxes, but the infection spread to other Android-based IoT products too, including telehealth devices, karaoke machines and digital signage. Google says the devices were used without their owners' knowledge for ad fraud, data exfiltration and routing unauthorised network traffic.
Android TV box botnet: what Google found
Google says the backdoor, tracked as XCPE, was designed to make money. According to the company, Videostrong sold access to criminal affiliates and loaded their malware modules onto infected machines. Those modules ran ad fraud, silently enrolled devices in residential proxy networks and pushed more malware onto compromised hardware.
The company was clear that this was not an accident. Google says the backdoor and botnet were intentionally developed, deployed and operated for financial gain, and that the campaign was not an isolated rogue insider or a development oversight.
- Roughly 1.3 million devices were compromised worldwide, according to Google.
- The malware was found built directly into many different device models and brands over multiple years.
- Besides TV boxes, infected hardware included telehealth devices, karaoke machines and digital signage.