Google's Threat Intelligence Group says it has shut down a massive botnet called x.cpe that ran on more than 1.3 million Android TV devices. What makes the case unusual is that these were Google-certified boxes, meaning they had passed the screening process required to use Google apps and branding.
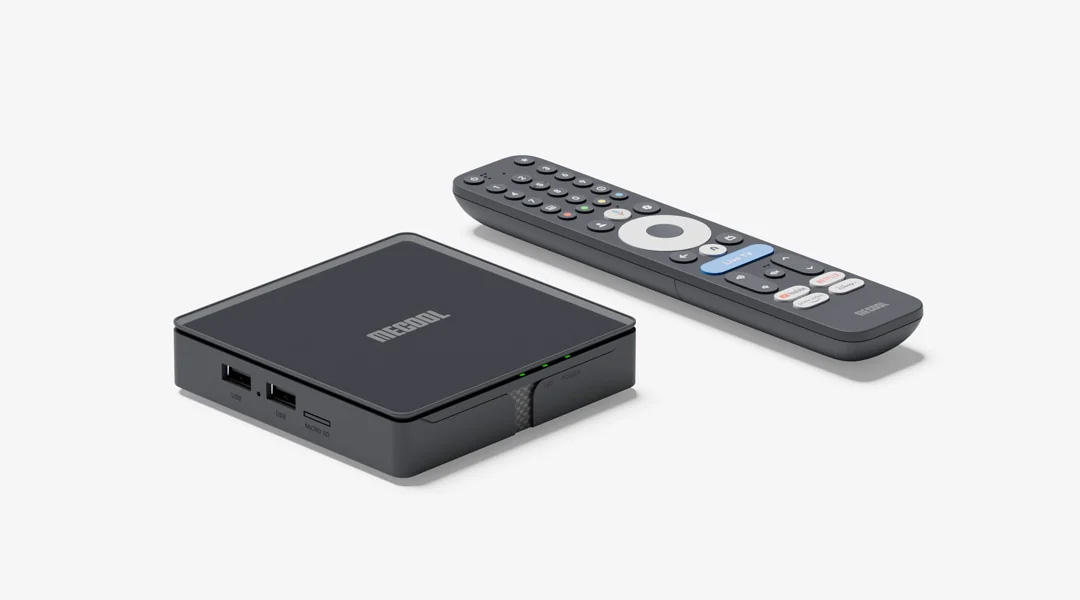
According to a detailed blog post from the Threat Intelligence Group, the operation was run by Shenzhen-based Videostrong Technology, whose devices are mostly sold under the MECOOL brand. Google says its screening missed the malware because of obfuscation techniques used by the company, and it has now ended its relationship with Videostrong over the campaign.
How the x.cpe botnet infected certified Android TV boxes
The malware did not ship active on the devices. Instead, Videostrong used a backdoor to remotely install it after the boxes were set up and online, which is how the compromised hardware got past certification in the first place.
Once a device connected to the internet, a stub application called x.cpe or com.oemservice would phone home. That package had no malicious capabilities of its own, but it carried the system-level permissions needed to install malware modules on command, and it disabled Play Protect so the silently installed packages would not be flagged.
- x.cpe ran on more than 1.3 million Android TV devices at its height, according to Google.
- Trend Micro counted 1,472,554 infected devices, somewhat higher than Google's estimate.
- Most infections were in Brazil, Malaysia, Iraq, Mexico and Taiwan, with tens of thousands also online in the US, Germany, the UK, Australia and Canada.