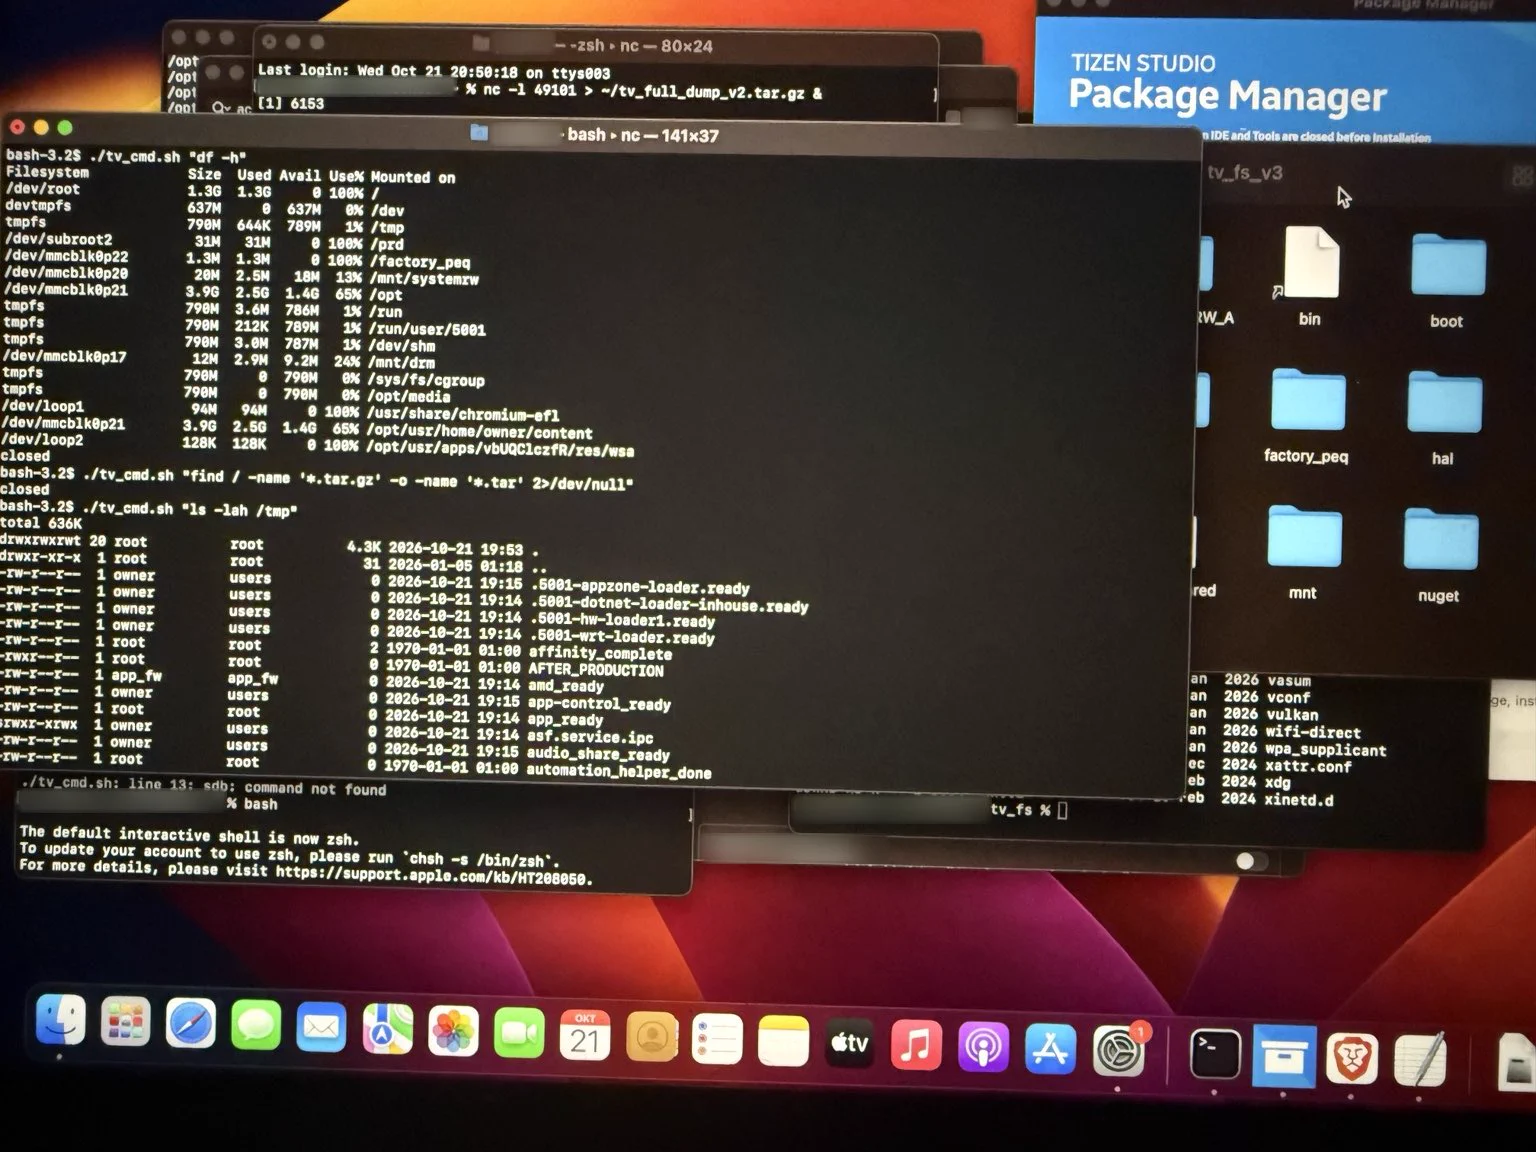
A researcher posting on X as log4j says he obtained a root shell on a relatively new 2025 Samsung TV, claiming he found what he calls a "privacy horror" inside the set. The post, dated October 21, 2026, says the work began after he kept receiving weirdly targeted ads on the television.
He says he first tried reversing the firmware, but found it protected with AES encryption and no accessible keys without physically opening the TV for UART or JTAG access. Instead of a hardware teardown, he says he turned to zero-day exploits to gain root access. The claim has drawn heavy attention, with the post showing more than 1.2 million views and thousands of replies and reposts.
Samsung TV root shell claims
The researcher has not yet published a full technical write-up, and the post reads as a teaser asking whether readers want one. No vulnerability details, affected model numbers, firmware versions or Samsung response have been shared so far.
What is described is a root shell, meaning privileged access to the TV's operating system. That level of access could in theory expose how a smart TV handles data, but the specific findings behind the "privacy horror" label remain unknown until the promised write-up appears.
- Target: a 2025 Samsung TV, described as relatively new
- Starting point: oddly targeted ads seen by the owner
- First attempt: firmware reversing, blocked by AES encryption
- Hardware route rejected: keys would need UART or JTAG access