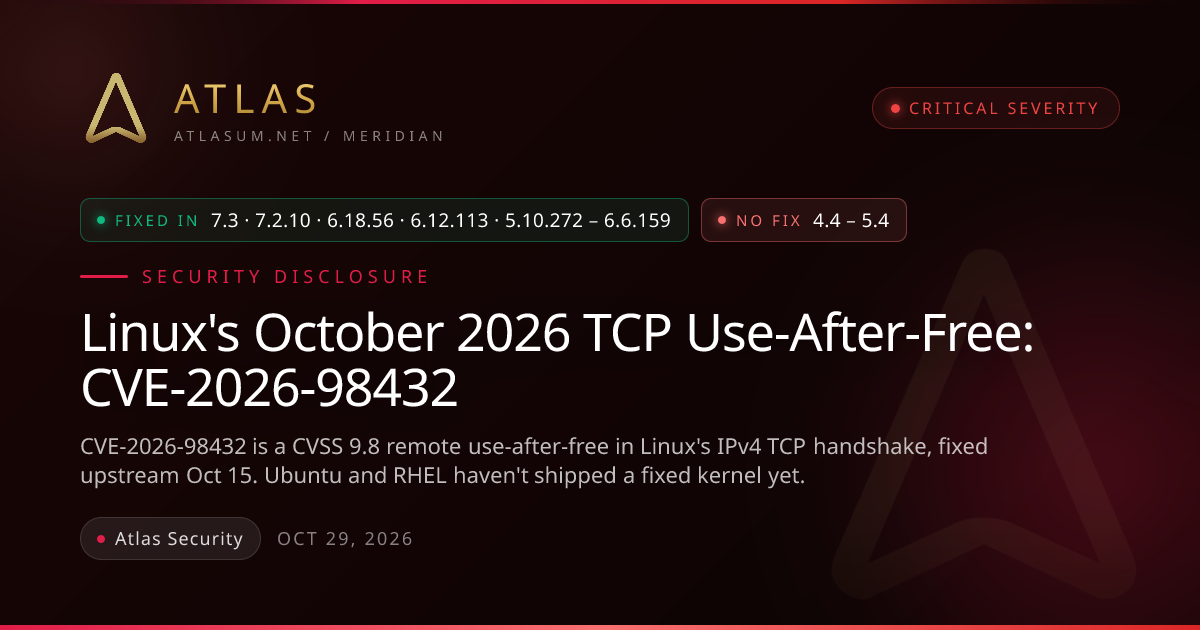
Ubuntu has still not released patched kernels for CVE-2026-98432, a critical Linux remote code execution flaw rated CVSS 9.8, almost three weeks after the vulnerability became known. According to freenode.net, no fixed kernel packages are available for the 22.04, 24.04 or 26.04 LTS releases, leaving administrators on those versions without a vendor update that closes the hole.
Until Ubuntu ships patched packages, every host running those LTS kernels remains exposed to whatever remote or local attack the CVE enables. The exposure is most serious for internet-facing servers and multi-tenant self-hosted systems that depend on Ubuntu's LTS kernels for isolation and privilege boundaries.
CVE-2026-98432: what we know
The flaw is tracked as CVE-2026-98432 and carries a CVSS score of 9.8, the highest severity band. That rating signals a vulnerability that can be exploited remotely with little or no authentication, which is why the missing patch has drawn attention from sysadmins running production workloads on Ubuntu LTS.
Ubuntu has not announced an ETA for the fixes, and no patched kernel packages have appeared for 22.04, 24.04 or 26.04 at the time of writing. The company has not publicly explained the delay.
- CVE-2026-98432: critical Linux remote code execution vulnerability
- CVSS score: 9.8
- Affected Ubuntu LTS releases without a fixed kernel: 22.04, 24.04, 26.04
- Status: no patched kernel package available, no ETA announced